What's new in PhishClean 1.3.0: see your protection working
A security extension that is doing its job is silent, and silence looks exactly like doing nothing. 1.3.0 makes the protection visible without making it noisy: a daily count on the toolbar, a weekly report, and a clear next step if you ever click something you should not have.
Rolling out now: 1.3.0 is live on Chrome and Firefox, and will be on Edge shortly. Your browser updates it automatically. As before, every check runs locally in your browser and nothing about the pages you visit leaves your device.
A daily count on the toolbar
The PhishClean icon now shows how many pages it checked today. The badge is green on a normal day and turns red on a day it blocked something. Only the number is stored, per day, on your device. No URLs, no page titles, nothing that says where you went.
Sites you have marked as trusted are skipped, so they are not counted either: the number is pages actually scanned, not pages visited.
A weekly safety report
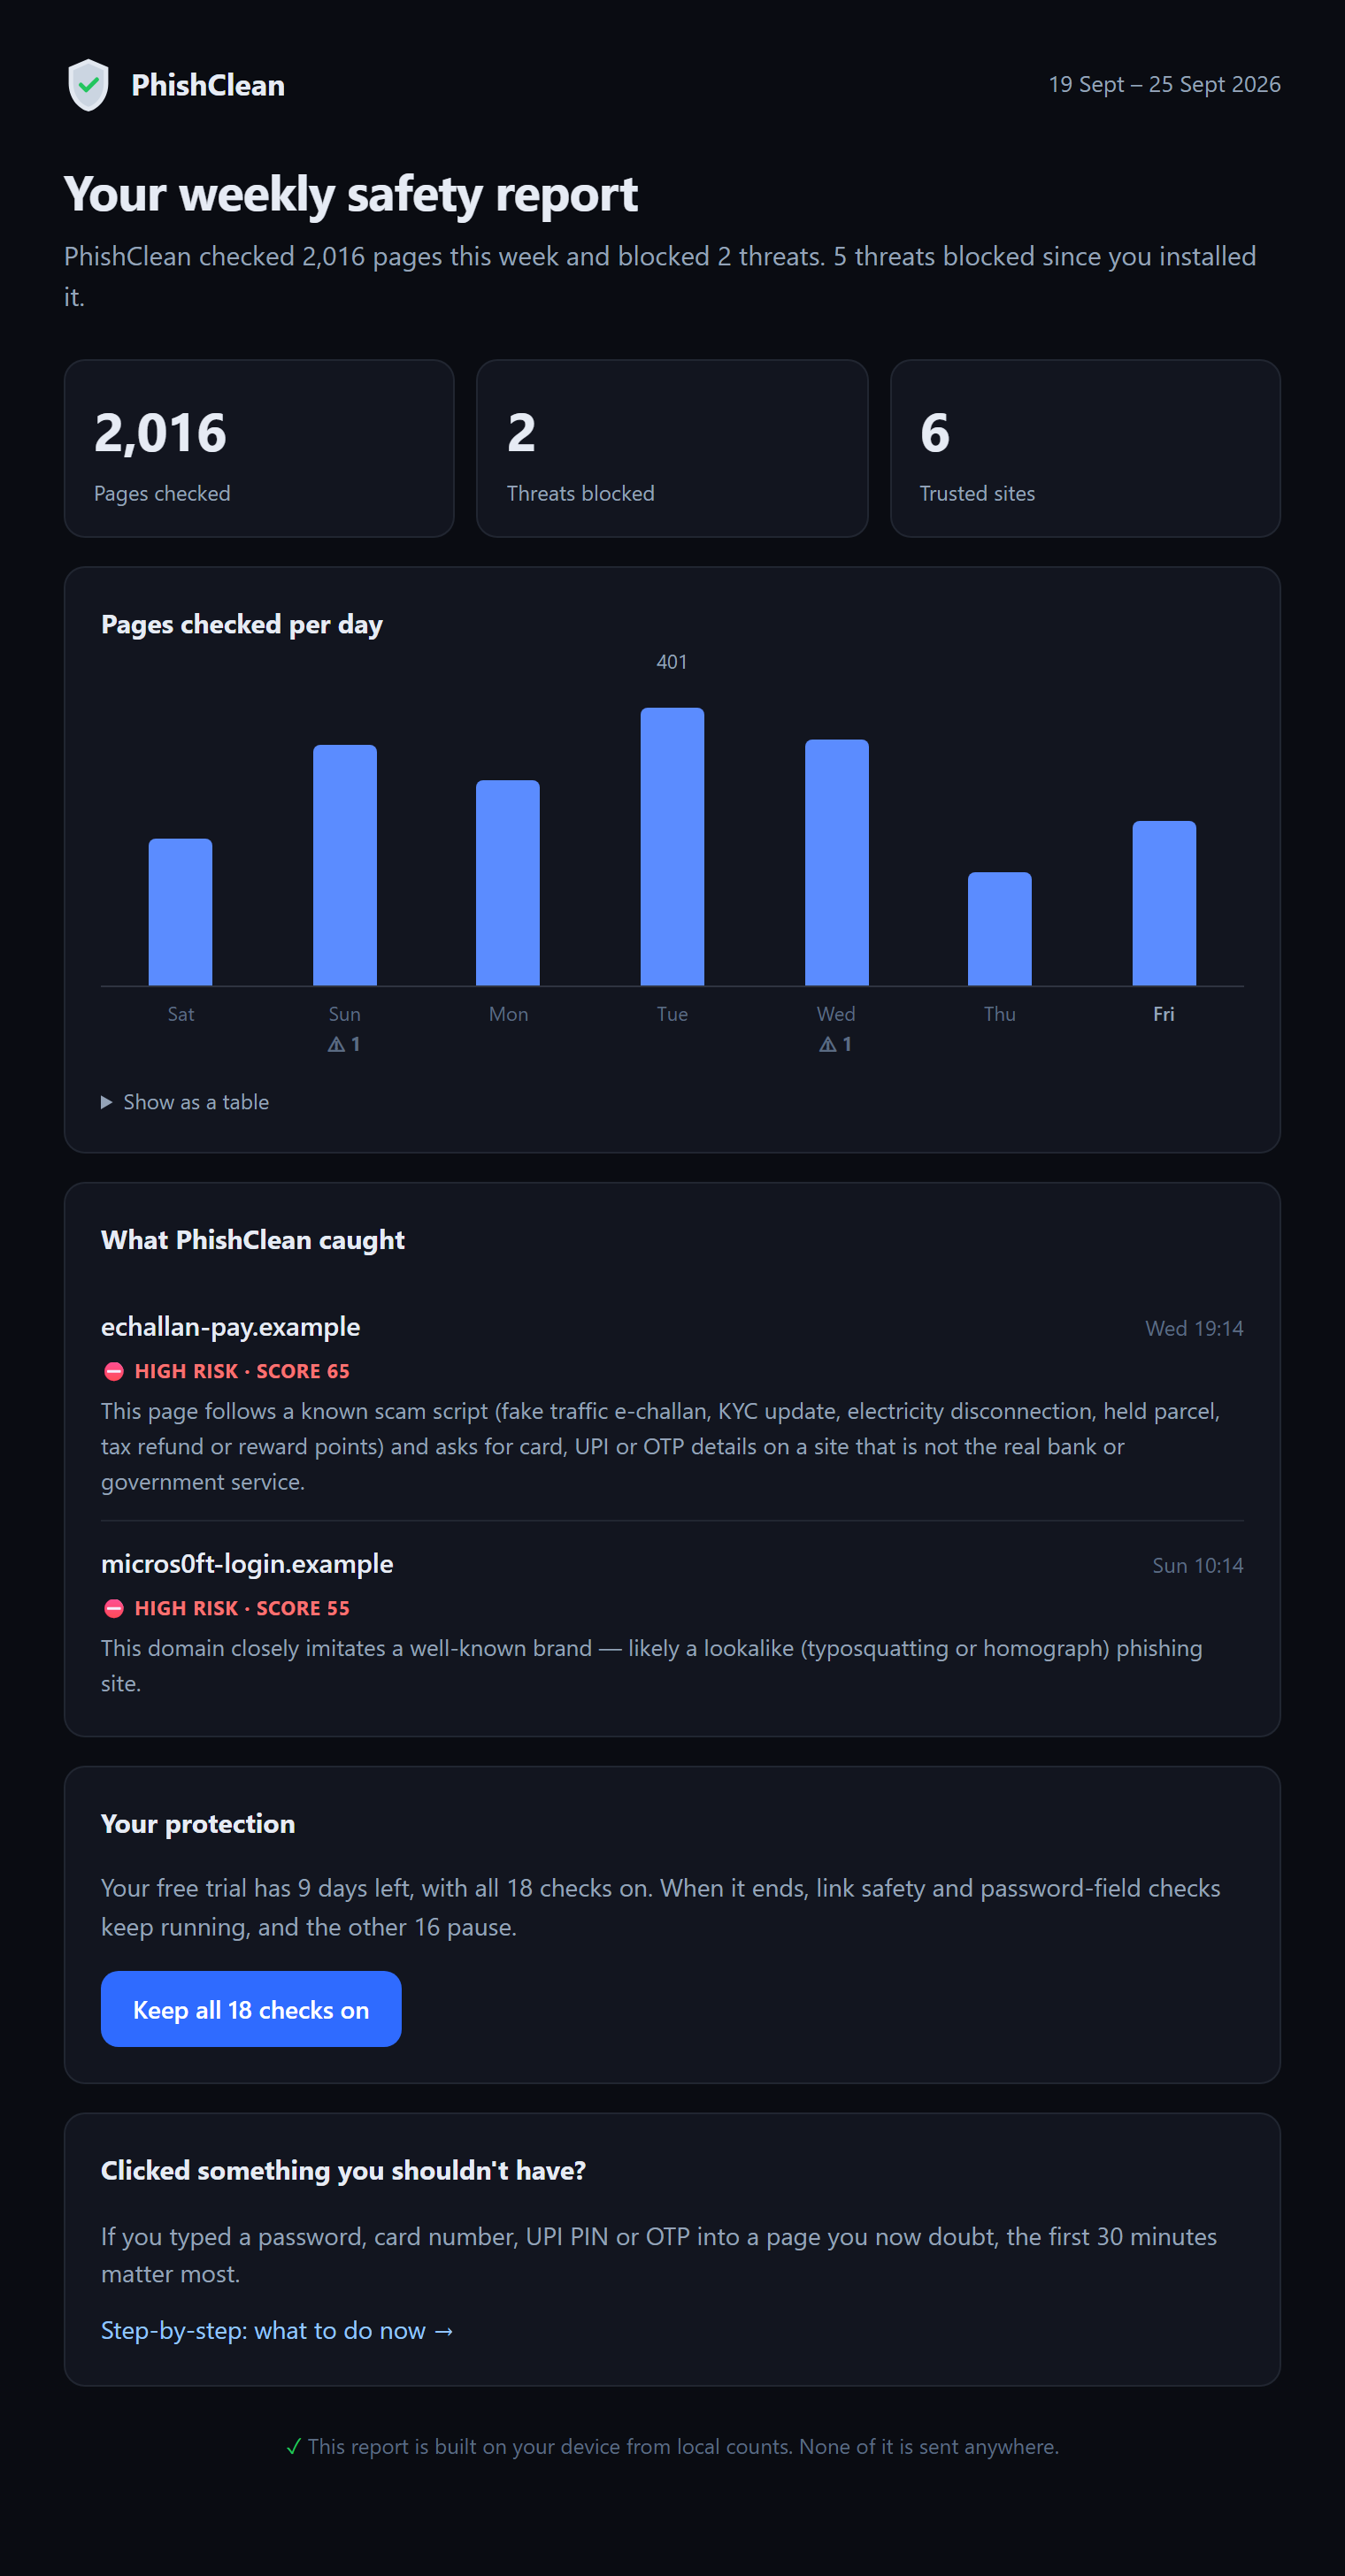
Once a week PhishClean sends one notification that opens a short report: pages checked each day, and what it caught. The report is built from the same local counts and is never sent anywhere. In a week you barely used the browser, there is no notification at all.
This release adds the "notifications" permission for the weekly report. It shows no warning at install and is used for nothing else.
"Clicked a bad link?" - what to do now
Warnings are only half of it. If you already typed a password or card number into a page before you realised, the next ten minutes matter. There is now a step-by-step recovery guide at /help/clicked-a-phishing-link: pick what happened, and it shows what to change first, who to call, and where to report it in India, the US, the UK, Canada and Australia. The popup and every warning link straight to it.
There is also a guide for India specifically, starting with the 1930 cybercrime helpline, because for UPI and card fraud the first hour decides whether the money can be frozen.
Catching the scams Indian users actually get
The most common scam pages in India are not fake login screens. They are fake traffic fines, KYC updates, electricity disconnection notices, parcel fees, tax refunds, FASTag recharges and bank reward points, each asking for a card number, UPI PIN or OTP. PhishClean now recognises these scripts, in English and Hindi, when they appear on a page that asks for payment details on a domain that is not the real service.
- Needs all three: the scam wording, a card, UPI or OTP field, and an unofficial domain. Real government and bank sites (gov.in, nic.in, bank.in and known official domains) are excluded.
- Indian banks and services join lookalike detection, so a domain imitating a major bank is flagged the way lookalikes of global brands already were.
- Part of the paid plan, and included in the 15-day trial.
Rupee pricing in India
Visitors in India now see and pay ₹149/month or ₹999/year. Everywhere else stays at $9/month or $59/year. The price is decided once, on our server, from your country, so the extension, the website and the checkout always show the same amount.
Smaller things
- The settings page and popup were rewritten to say each thing once, with one consistent text size, so they look the same in Chrome, Firefox and Edge.
- After the trial, the settings page lists what is still on and what is paused side by side.
- The "Contact support" link in the popup now opens the contact page. Previously it did nothing.
Try every check for 15 days
No account needed to start, and none needed to keep going. Install, browse, and watch the count go up.
Install PhishClean freeLast updated: